
Your release schedule rewards speed, but users expect restraint. An app can leak personal details simply by working as designed; no one has to break in. An encrypted health event, intact and secure, can still land at an advertising platform. Your development team should look at technical defenses and data-handling decisions as two separate questions. In production, engineers watch what the app collects and who ends up receiving each transmission. Legal questions go to the lawyers.
Data security and privacy solve different problems
Security controls protect against unauthorized access
Security means keeping information restricted and accurate. Encryption scrambles readable data. Authentication checks who someone is. Access restrictions decide who can reach what. All of it still matters.
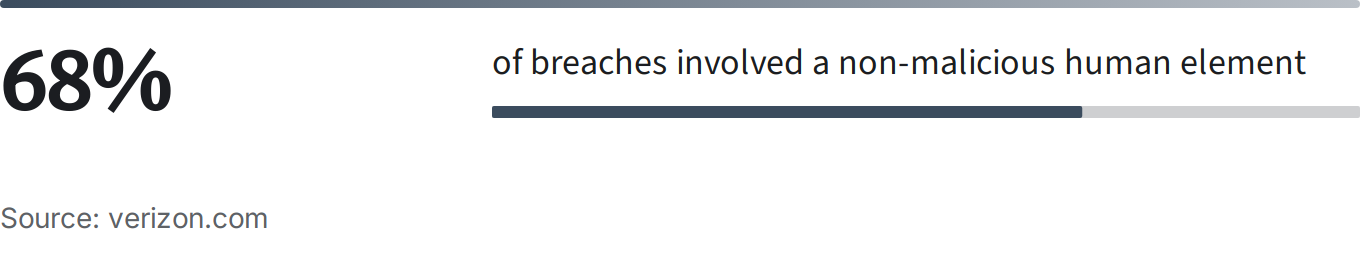
Verizon’s 2024 Data Breach Investigations Report covered 30,458 security incidents and 10,626 confirmed breaches across 94 countries, and found that 68% of breaches involved a non-malicious human element. That finding supports configuration checks and employee training. For a development review, treat those figures as security context rather than as a count of privacy failures or evidence about a particular app’s intended data flows.
Privacy controls govern appropriate handling
Privacy is about what you collect, why, who receives it, and how long you keep it. Encryption cannot justify collecting data you never needed, and it cannot stop an authorized software development kit, which is vendor code inside the app, from pulling in more than it should. Encryption during storage keeps records safe on disk. Encryption during transfer guards network traffic. Neither answers the question of whether your app should keep an address on file after a customer deletes their delivery profile. No intrusion is required here.
How ordinary app components disclose personal data
Pixels and third-party SDKs
A tracking pixel fires off visit or button events, and identifiers or form details sometimes ride along. SDKs can read app events and device data too. Check the payloads, meaning the transmitted contents, against your consent and recipient settings.
In its 2023 BetterHelp enforcement announcement, the FTC alleged the company shared sensitive health information with advertising platforms despite its own privacy promises.
Logs and exposed analytics dashboards
Verbose logs pick up email addresses and access tokens, credentials that authorize requests. A public dashboard link or weak login can lay your analytics bare without anyone ever touching the production database.
Permissions that exceed the feature
Ask for device permissions only when the feature actually needs them, and make revocation work. Photos, contacts, the microphone: each deserves a reason. Question a weather widget that wants continuous location access.
| Component | Privacy failure to inspect | Development check |
|---|---|---|
| Tracking pixel | Sensitive fields included in event payloads | Inspect runtime network requests |
| Third-party SDK | Undocumented collection or forwarding | Review code, configuration, and recipients |
| Application log | Personal data retained in plain text | Test redaction and retention settings |
| Analytics dashboard | Public links or excessive account access | Verify authentication and sharing controls |
| Device permission | Access exceeds the active feature | Request access only when needed |
A two-track review for development teams
Map every data path
- Inventory collected data and its purpose.
- Follow every network destination.
- Watch what SDKs do at runtime.
- Verify log redaction and retention.
- Compare permissions with active features.
Inspect actual traffic while the app runs. The OWASP Mobile Application Security project offers practical resources for testing app controls, though it will not certify your consent screens. Repeat these checks after users refuse or revoke consent. Remove unnecessary fields. When forwarding continues unexpectedly, disabling the vendor component responsible for the request is often the fix.
Test collection against user expectations
Compare observed behavior against your consent screens and published disclosures. Block unnecessary transmission before release rather than documenting it afterward in a privacy notice.
When data privacy and security lawyers may matter
Respond in a deliberate order
- Stop unnecessary collection or sharing without destroying evidence.
- Preserve configurations, notices, relevant logs, and communications.
- Determine what data moved and who received it.
- Assess notification requirements and contractual or legal obligations by jurisdiction.
Notification rules differ by jurisdiction, and some run on clocks measured in days. Once you preserve the records above, data security privacy lawyers can assess which deadlines and obligations apply to your situation.
Outcomes depend on the facts and the governing jurisdiction.
| Developer question | Decision criteria and evidence |
|---|---|
| What can counsel assess after technical triage? | Provide the disclosure, preserved evidence, affected data, recipients, and jurisdictions. Counsel can then identify potentially applicable laws and explain response options. Evidence sources: configurations, notices, relevant logs, and communications. |
| When should the team seek legal guidance? | Consider legal guidance when sensitive data or measurable harm is involved, especially when consent or notice obligations are disputed. Decision sources: the data inventory, consent records, published disclosures, contracts, available evidence, and governing law. |
| What should developers verify before escalation? | Reproduce the transmission, record its payload and destination, and test behavior after consent refusal or revocation. Technical sources: runtime network requests and the OWASP Mobile Application Security project cited above. |
| What should the team confirm before engaging outside counsel? | Define the incident scope and request written fee terms. Cost depends on the complexity and the arrangement. Decision sources: the documented incident scope and proposed engagement terms. |
| Which confidentiality failures should developers flag? | Flag disclosed health details, exposed employee records, improperly shared location histories, published financial records, and unauthorized access to private communications. Evidence sources: payload captures, access logs, dashboard settings, and recipient records. |
Build confidence beyond encryption
Keep apps fast while limiting collection and checking vendor behavior against what users agreed to. Security checks restrict unauthorized access. Privacy checks challenge unnecessary sharing. Both belong in your release process. Apps earn confidence when teams protect data and ask whether each data flow should exist at all.